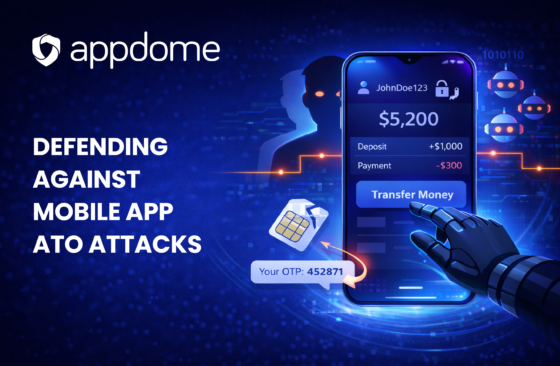
Defending Against Mobile App Account Takeovers (ATO) in 2026
Learn how to stop mobile app account takeovers in 2026. Block credential stuffing, mobile bots, emulators, and malware with persistent identity and real-time, in-app defenses.
Appdome lets you pair mobile device fingerprinting with the most comprehensive threat intelligence in the industry to stop mobile fraud with ease. Scale device reputation fast. Identify genuine, fake, and at-risk devices, sessions, and accounts during mobile onboarding, login, and transactions.
Appdome creates OS-independent, immutable device fingerprints for each mobile device that runs your Android & iOS applications. Each device identity survives device resets, app uninstalls, and other techniques. Use this unique Device ID to bind accounts and application histories, creating durable protection against mobile fraud, promo abuse, and ATOs.
Learn More >
With Appdome, each device fingerprint accumulates a device history, including validated identity, device properties, application lineage, and up to 400 mobile threat signals, building a durable reputation across installs and applications. Use this device reputation to identify good, bad, and at-risk sessions, accounts, and transactions with ease.
Learn More >
Appdome's MobileRISK™ API combines billions of device fingerprints and trillions of threat signals into ready-made profiles, agentically generating severity and risk scores that mobile brands can tap into to stop KYC fraud, device spoofing, GPS spoofing, account farming, mule accounts, deepfakes, and rogue AI agents before tehy impact your business.
Learn More >
Appdome gave us the immutable device binding and deep device intelligence we needed to stop fake logins and deepfakes.”
CISO, Digital Banking Platform
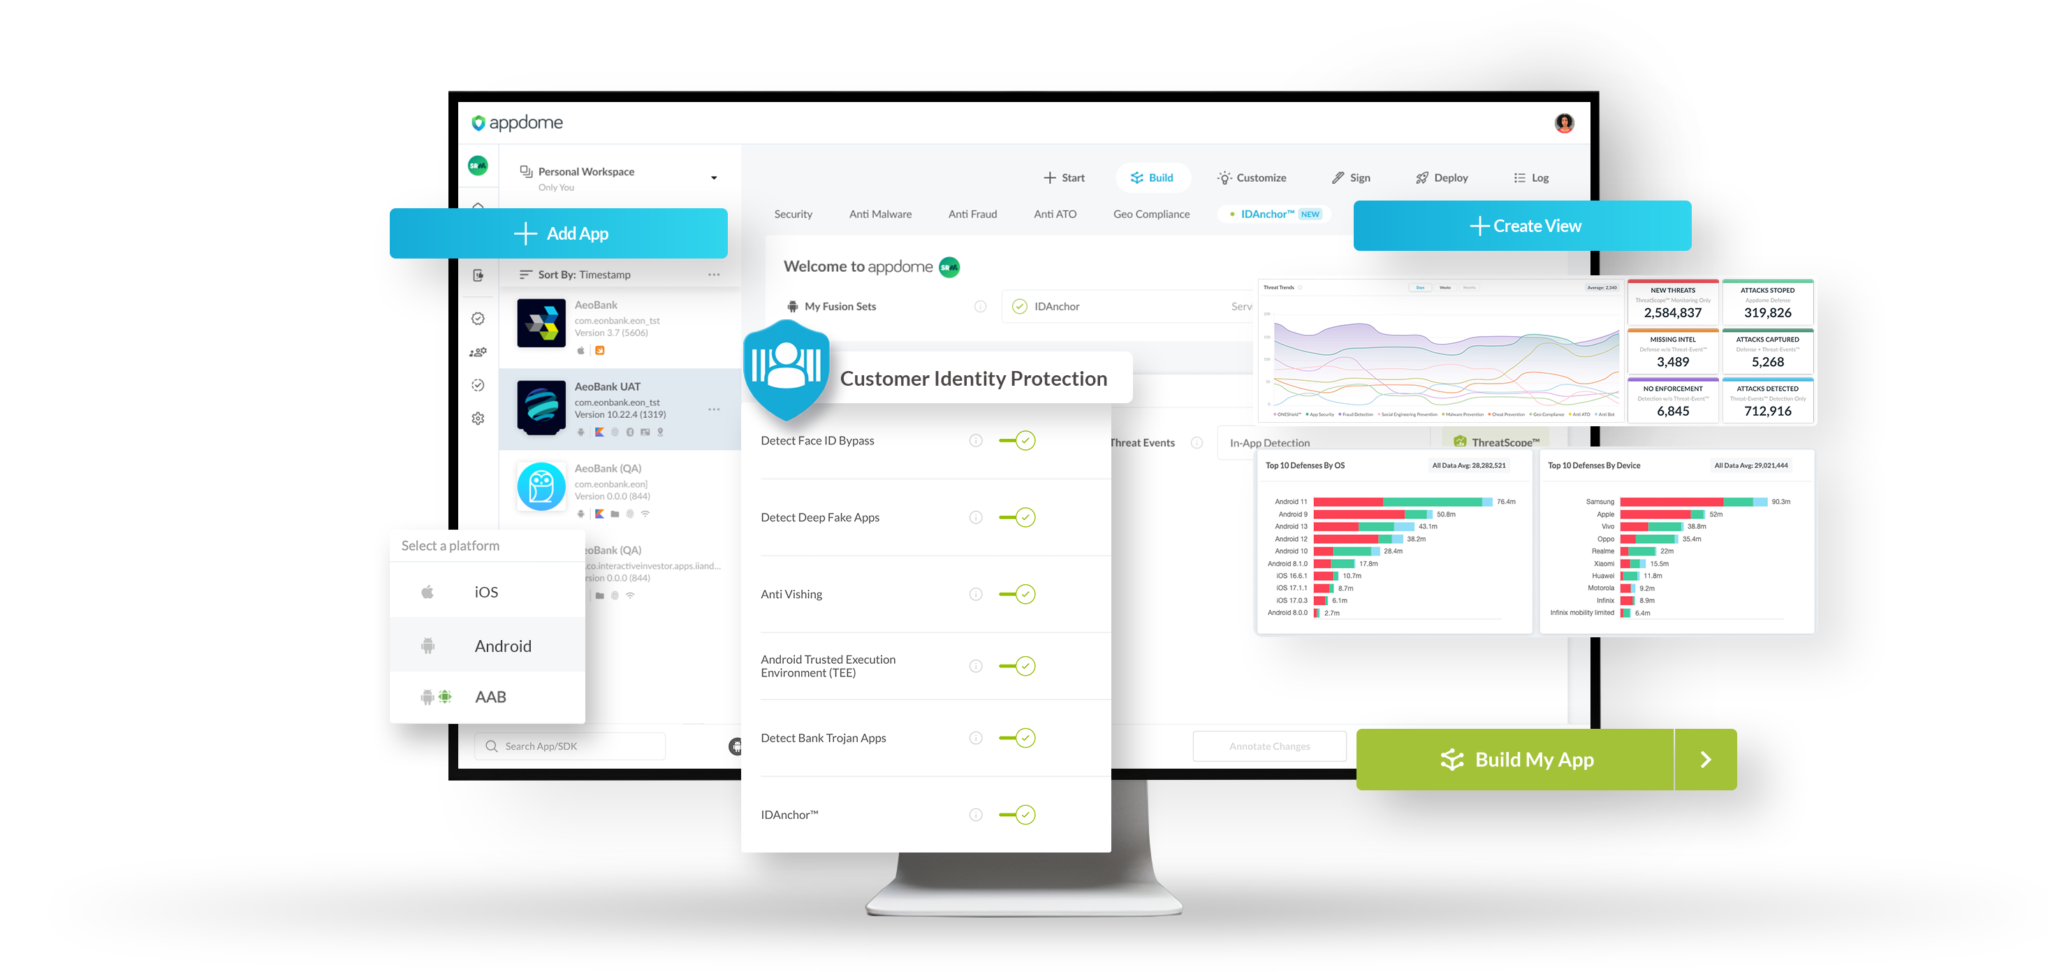
Start a 30-Day Free Trial of Appdome and leverage the power of AI to build device fingerprinting and mobile reputation into your Android & iOS apps - fast. Each feature is built by Appdome to match your app's code and structure, eliminating manual work, SDK implementations, code maintenance, and other efforts. Scale up your own device profiles in minutes, monitor attacks, and click-to-respond to the top attack vectors on demand.
With Appdome, you replace manual work with agentic automation and deliver device identity and reputation quickly and easily. On Appdome, you choose the policy, and the platform does the work. With each Android and iOS build, the platform codes, maintains, and updates the device and application identity signals framework for you. Agents are available to validate implementations, detections, or attacks in real time. Review the Device Fingerprinting options below and contact us to put them to work in your app.
IDAnchor™ generates unique mobile device and application fingerprints from each device running a protected mobile application. Over the lifetime of a mobile end user, these identifiers provide continuous lineage, threat history, and reputation data to detect mobile fraud, ATOs, scams, and abuse. Any unauthorized sign-in, synthetic identity, credential reuse, substitute or Trojan apps, or fake and spoofed devices will create a break or mismatch in the chain of trust and instantly signal a device, account or transaction risk or threat. Accumulating threat history allows mobile brands to see at-risk devices with ease.
Learn How >
Combine IDAnchor's mobile identities with 400+ mobile fraud and threat signals to build rich and dynamic device intelligence for every Android & iOS device running your Appdome-protected app. Each profile distinguishes legitimate and safe devices from fake, high-risk, or compromised devices, and provides detailed device intelligence on the state of the device, its properties, and any on-device threats. With precise device risk profiles, mobile apps can tune authentication, payments, and account controls to match the true risk of every session—maximizing security and minimizing friction.
Learn How >
IDAnchor™ provides True Device API™ to continuously verify mobile device make, model, chipset, OS, and other metadata over time and return a confidence score that the device properties remain true and not spoofed at the time of the request. This allows mobile brands to identify the specific device property that is changed, updated, manipulated, or spoofed. This accurate, tamper-resistant intelligence enables mobile developers and fraud teams to reduce false positives and false negatives, and to screen for malicious devices with confidence without disrupting good users.
Learn How >
IDAnchor's Device IDs are generated per Android or iOS device to provide a persistent, verifiable substrate to bind each mobile end user or account to a specific mobile device. Device binding is an effective mechanism for tracking users and ensuring that login and other critical workflows occur on a trusted device. For example, when an unrecognized or new device is used to sign in, IDAnchor instantly flags the new device for the affected user, allowing the app to generate sign-in alerts and adaptive security actions to confirm the authenticity of the user or session.
Learn How >
IDAnchor is built on the foundation that mobile devices and applications will evolve over time. Users will update their devices, update applications, upgrade operating systems, and make other changes. To accommodate this reality, Appdome provides Device MATCH and Instance MATCH APIs to evaluate all of these changes against all updates and upgrades to the same mobile apps, devices, and operating systems used by the brand's mobile end users and all mobile apps, devices, and OSs across Appdome's 4 billion installs, in each case for signs of fraud or manipulation.
Learn How >
IDAnchor™ provides continuous mobile device reputation by attributing activities and threats to immutable Device IDs over time. As each mobile device builds a risk profile, it is benchmarked and scored, allowing the device's reputation to be used and shared across sessions, applications, and device instances. Each device carries a dynamic reputation score that reflects its real-world activity and threat history across multiple apps. This shared intelligence empowers mobile brands to instantly identify bad actors, block fraud faster, and approve trusted users with confidence.
Learn How >
IDAnchor™ can build a dynamic risk profile for each user account. Using standard authentication data such as User_ID, authentication tokens, and related headers, IDAnchor can correlate threat telemetry to each account. This allows mobile businesses to identify high-risk accounts—those associated with suspicious devices, failed authentications, or policy violations—and take adaptive action in real time. With IDAnchor, every account carries its own verified device lineage and evolving risk profile, giving fraud and security teams continuous visibility into where identity threats emerge.
Learn How >
IDAnchor™ enables privacy-safe mobile device tracking that eliminates device resets, bot-generated clicks, fake referrals, promotion stacking, and similar tactics and preserves trust, all while powering ads, promotions, and loyalty programs. By binding every engagement to a verified device identity—not cookies or ad IDs—IDAnchor gives marketers and developers a reliable way to measure conversions, validate redemptions, and prevent offer abuse. This persistent, tamper-resistant tracking ensures that rewards and promotion inventories reach real users on real devices, boosting campaign integrity and ROI without sacrificing user privacy.
Learn How >
With Appdome, you can augment and support your customer identity with immutable mobile device and application IDs, without sacrificing your engineering freedom, development choices, or the user experience. Leverage Appdome’s identity chain of trust to bind customer identity to verified mobile identity that cannot be spoofed or reset. Appdome is fully compatible with all Android & iOS apps and has plugins to your existing DevOps stack, including CI/CD, test automation, release management, and more.
Get a price quote and start saving money on Device Identity today and defend your brand against identity fraud, identity theft, fake identity and other mobile identity threats. Defense helps brands save $millions of dollars by avoiding unnecessary SDKs, server-side deployments, engineering work, support complexity, code changes and more.

Learn how to stop mobile app account takeovers in 2026. Block credential stuffing, mobile bots, emulators, and malware with persistent identity and real-time, in-app defenses.

Android bootloader integrity is often reduced to a locked or unlocked state. This article explains why that model fails and how contextual bootloader signals improve identity and session trust.
For years, fraud prevention solutions have tried to use Device IDs to bind (or link) a user’s account or session to a specific device to prevent unauthorized access from other devices. However, until recently, Device IDs lacked persistence and the broad threat context needed to stop fraud and ATOs …
Use these step-by-step guides to learn how to use Appdome and agentic automation to build Mobile Identity & Reputation in your Android and iOS apps. Each Mobile Identity & Reputation knowledge base article illustrates how you set up the Mobile Identity & Reputation policy, and Appdome builds, maintains, and updates each Mobile Identity & Reputation protection in your mobile apps for you – automatically. Advanced topics are also covered, such as obtaining threat data from Mobile Identity & Reputation events, session risk, device reputation, user experience options during attacks, CI/CD integration, code signing, Mobile Identity & Reputation compliance validation and tracking, and other DevOps features available on Appdome. Learn more about using Appdome in your CI/CD today!