Understanding Appdome DefenseOS™
What is DefenseOS™?
DefenseOS™ is Appdome’s governed execution environment for security, anti-fraud, anti-bot, compliance, and other defense plugins in protected mobile apps. It coordinates how these plugins initialize, execute, communicate, and use application resources at runtime.
DefenseOS manages defense workloads within the app to help prevent conflicts between protections and minimize their impact on app performance and stability. It is integrated automatically into Appdome-protected apps during the build process and does not require developers to manually manage the execution of individual defense plugins.
What Does DefenseOS™ Provide?
DefenseOS provides a shared execution layer for Appdome defense plugins, including:
- Defense orchestration – Coordinates the initialization, prioritization, and execution of defense functions.
- Resource management – Manages CPU, memory, and network usage across defense workloads.
- Workload scheduling – Controls when and how defense tasks execute to reduce resource contention and conflicts.
- Runtime stability – Supervises defense workloads to help maintain app performance and continuity.
- Secure communication – Provides secure communication between defenses and detection methods.
- Policy management – Manages defense policy activation and runtime changes.
Viewing DefenseOS™ in Certified Secure™
DefenseOS™ is included by default in every app built on the Appdome platform. The DefenseOS modules included in each protected app are listed in the Certified Secure™ certificate generated with the build.
The DefenseOS section of the certificate provides a record of the DefenseOS modules included in the app. Use the table below to learn more about each module listed in the certificate.
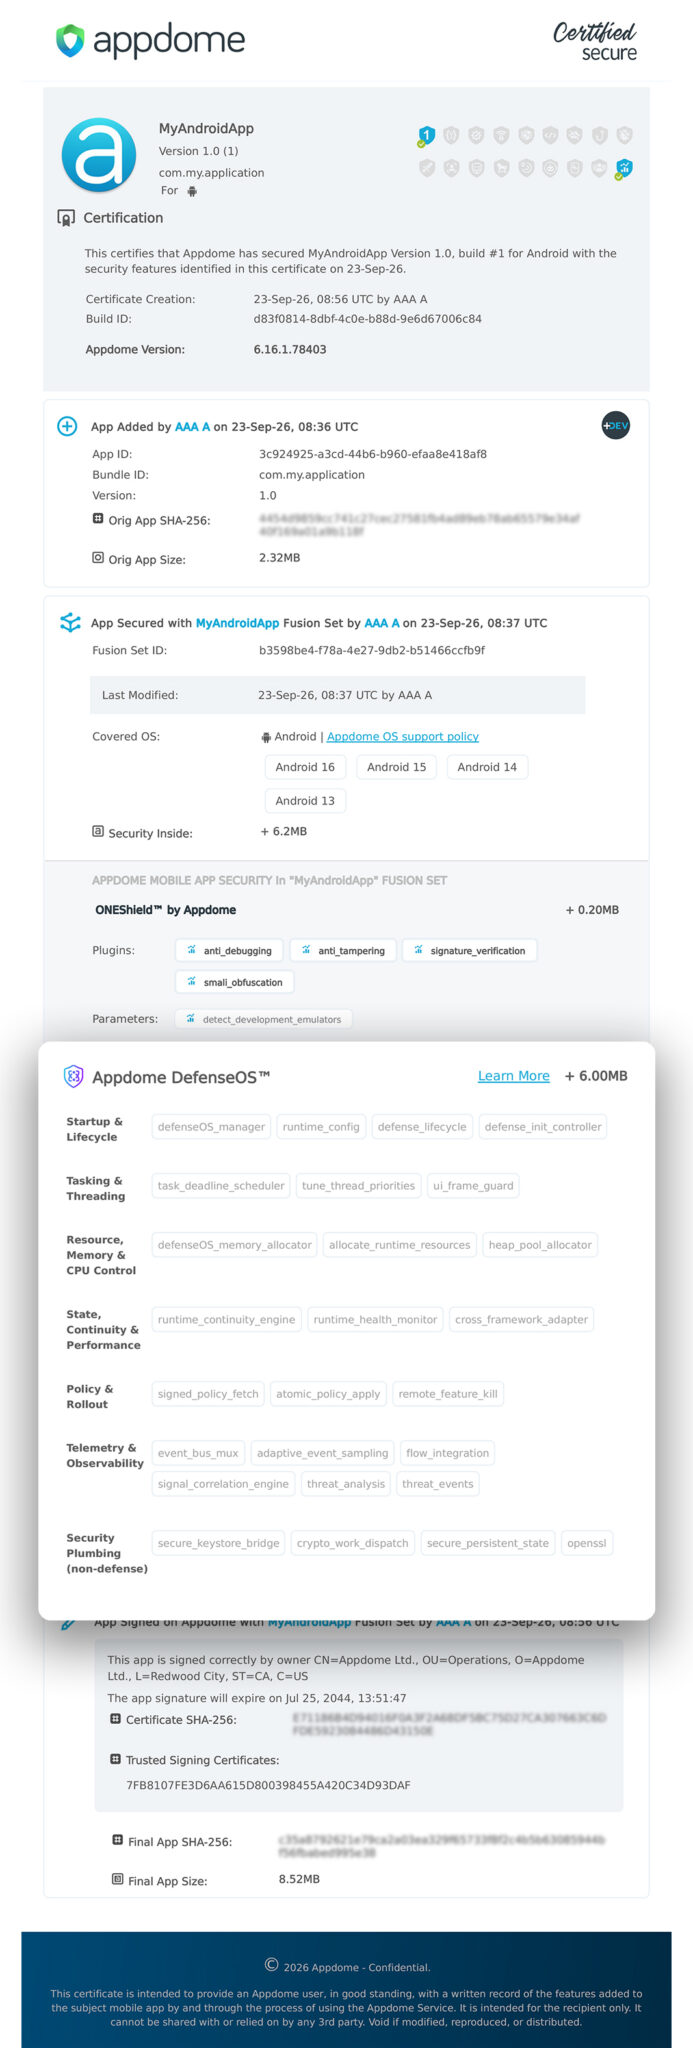
Viewing DefenseOS™ Modules
DefenseOS™ is included by default in every app built on the Appdome platform. The DefenseOS modules included in a protected app are listed in the Certified Secure™ DevSecOps attestation generated with each build.
Startup & Lifecycle
| DefenseOS™ Plugin | Description |
| defenseOS_manager | Core runtime manager that initializes, orchestrates, and terminates detection/defense components, routes decisions and policy enforcement. |
| runtime_config | Runtime configuration bundle, includes versioning, defense posture coded to app, policy layout, and compatibility metadata. |
| defense_lifecycle | Protects defense lifecycle transitions (init/stop/re-init) against manipulation and ensures safe ordering with OS and Application events. |
| defense_init_controller | Dynamically controls feature initialization across launch/resume/process recreation; improves TTI and startup CPU, reduces main-thread contention, and avoids memory spikes that impact FPS. |
| defense_startup_profiler | Profiles cold-start/first-interactive paths to identify slow init work and defer non-critical tasks; improves TTI, lowers CPU bursts, reduces main-thread work, and avoids memory spikes that hurt FPS. |
| defense_process_tracker | records background / foreground / process death continuity for performance and security controls |
| defense_plugin_lazy_loader | Defers loading of heavy modules on constrained devices; reduces startup CPU and memory pressure to improve TTI, FPS stability, and main-thread responsiveness. |
| defense_config | Protects sensitive in-app configuration (threat policies, client cert material, keys, endpoints, feature flags) from extraction and tampering. |
| loader_code_integrity | Ensures integrity of loader/runtime code sections (e.g., text segment) to detect patching, inline hooks, and code modification. |
| optimized_memory_scan | Platform-tuned memory scanning (rate-limited, region-aware) to support detection features with reduced overhead. |
Tasking & Threading
| DefenseOS™ Plugin | Description |
| task_deadline_scheduler | Schedules work within OS constraints (WorkManager/BGTaskScheduler); prevents main-thread overload, smooths CPU usage, and protects TTI/FPS by deferring non-urgent tasks and limiting memory churn. |
| tune_thread_priorities | Tunes priority/QoS to protect the main thread; improves FPS and responsiveness by reducing CPU contention and avoiding background bursts that cause memory and scheduling pressure. |
| ui_frame_guard | Moves heavy work off render-critical paths; protects FPS by reducing main-thread blocking, lowering CPU spikes, and preventing transient memory pressure during frames. |
| allocate_runtime_resources | Enforces CPU/RAM/network budgets with degrade modes; stabilizes FPS by protecting main-thread time, reduces memory pressure, and maintains TTI under load. |
| crypto_work_dispatch | Dispatches crypto workloads safely/off-main-thread; supports batching and preferential hardware-backed primitives when available. |
| watchdog_timeout_guard | prevents ANR / iOS watchdog termination |
| cross_feature_ipc | Secure inter-module communication (message validation, schema/versioning, isolation boundaries). |
Resource, Memory & CPU Control
| DefenseOS™ Plugin | Description |
| DefenseOS_memory_allocator | memory scanning (rate-limited, region-aware) to support detection features with reduced overhead. |
| allocate_runtime_resources | Enforces CPU/RAM/network budgets with degrade modes; stabilizes FPS by protecting main-thread time, reduces memory pressure, and maintains TTI under load. |
| heap_pool_allocator | Pools objects to reduce allocations; lowers memory churn and GC/ARC overhead, reduces CPU cost, and improves FPS and main-thread smoothness (especially during startup/TTI). |
| multi_tier_cache | RAM/disk caching with TTL eviction; reduces CPU recomputation and I/O, lowers memory thrash, improves TTI by avoiding repeated work, and helps FPS by minimizing main-thread stalls. |
| backpressure_controller | Applies backpressure to queues to prevent runaway memory growth; smooths CPU usage, protects FPS by limiting bursty processing, and avoids main-thread overload that delays TTI. |
| lock_contention_guard | Detects lock hotspots and reduces contention; improves FPS and responsiveness by protecting main-thread scheduling, lowering CPU waste on waiting/spinning, and reducing cascading memory pressure. |
Network Resilience
| DefenseOS™ Plugin | Description |
| smart_retry_polling | Adaptive retry/polling tuned by errors/connectivity/app state; reduces CPU wakeups, avoids main-thread work, prevents memory build-up, and improves TTI/FPS by smoothing background load. |
| adaptive_retry_backoff_timeouts | Adaptive retry/backoff/timeout control; reduces CPU churn and thread wakeups, avoids queue growth (memory), and protects FPS/TTI by limiting burst retries that steal main-thread time. |
| offline_persistent_queue | Disk-backed buffering during connectivity loss; prevents in-memory queue growth, reduces CPU thrash from repeated retries, avoids main-thread stalls, and stabilizes TTI/FPS under poor networks. |
| optimize_network_queue | Batching/compression/bandwidth shaping; lowers CPU overhead, reduces memory buffering, avoids main-thread spikes, and improves TTI/FPS by smoothing send/encode work. |
| network_adaptive_throttler | Throttles uploads by connectivity/cost/bandwidth; reduces CPU and memory pressure and prevents background bursts that can degrade FPS and delay TTI. |
| io_batcher | Batches small disk/network I/O; reduces syscalls/wakeups (CPU), lowers contention, avoids main-thread stalls, and reduces memory pressure from excessive buffering—improving FPS and TTI. |
| cookie_manager | Coordinates cookie changes across multiple in-app cookie managers; resolves inclusion, removal, and conflicts so session cookies stay consistent across frameworks. |
| secure_webview_files | Enables WKWebView to securely load encrypted local in-app files so hybrid web content works under filesystem encryption. |
| secure_webview | Applies Appdome network and EMM policies to off-process WebView components so in-app browsing stays under the same secure path. |
State, Continuity & Performance
| DefenseOS™ Plugin | Description |
| runtime_continuity_engine | Preserves runtime continuity across relaunches/upgrades; improves TTI by avoiding repeated cold work, reduces CPU spikes on restart, and controls memory usage by restoring only needed state safely. |
| runtime_health_monitor | Detects stalls/starvation/failures and triggers self-heal; protects FPS and main-thread responsiveness by preventing runaway CPU loops and memory leaks, and maintains TTI by recovering quickly from degraded states. |
| cross_framework_adapter | Adapts modules across hybrid frameworks; reduces integration overhead and avoids framework-specific main-thread stalls, helping TTI, FPS, CPU, and memory predictability |
| platform_capability_probe | Detects OS/hardware/permission availability; selects efficient implementations to reduce CPU and memory overhead and avoid main-thread slow paths that hurt TTI/FPS. |
| power_mode_adapter | Adapts execution under Doze/Low Power Mode; reduces CPU bursts and background wakeups, avoids main-thread contention, and keeps FPS/TTI stable under power constraints. |
| oem_compat_shims | mobile device- or OS-specific registry |
| app_traits_customization | Applies per-app tuning; optimizes CPU/memory tradeoffs to protect FPS and main-thread time while meeting TTI targets on different device classes. |
| up_to_date_toolkit | Maintains compatibility/version gating; avoids slow fallback paths that increase CPU and main-thread work, preventing regressions in TTI/FPS and memory behavior. |
| kotlin_defense_plugin | Kotlin compatibility layer; reduces main-thread overhead from reflection/coroutines edge cases, improving CPU efficiency and preventing memory churn that can degrade FPS and TTI. |
| swift_defense_plugin | Swift compatibility layer; reduces ABI/runtime edge-case overhead and avoids main-thread slow paths, improving CPU efficiency and preventing memory spikes that can degrade FPS and TTI. |
Policy & Rollout
| DefenseOS™ Plugin | Description |
| signed_policy_fetch | retrieves and verifies defense policies |
| atomic_policy_apply | activates policies without race conditions |
| remote_feature_kill | immediate disable with safe fallback |
| anti_store | Blocks unauthorized publishing of diagnostic or Build2Test apps to public stores so test builds can’t ship as production. |
| automation_browserstack | Build2Test trust adapter for BrowserStack; suppresses vendor-environment false positives so secured apps can run in that lab. |
| automation_common | Shared Build2Test trust rules common to all automation vendors. |
| automation_saucelabs | Build2Test trust adapter for Sauce Labs; allows secured apps to run in Sauce Labs without false-positive enforcement. |
| automation_lambdatest | Build2Test trust adapter for LambdaTest; allows secured apps to run in LambdaTest without false-positive enforcement. |
Telemetry & Observability
| DefenseOS™ Plugin | Description |
| event_bus_mux | Normalizes/merges event streams with ordering/backpressure; prevents memory queue blowups, reduces CPU overhead, and avoids main-thread contention—protecting FPS and TTI. |
| adaptive_event_sampling | Dynamically reduces event volume by device class/risk; lowers CPU and memory overhead, prevents background bursts, and protects main-thread time to maintain FPS/TTI. |
| flow_integration | integrates detections/defenses into selected runtime flows to enforce detection/protection gates and collect signals. |
| signal_correlation_engine | Fuses multiple runtime signals into decision objects (risk scoring, confidence, suppression rules). |
| threat_analysis | Evaluates collected signals to identify threats and produce enforcement decisions. |
| threat_events | Delivers in-app Threat-Event™ signals so detections can notify, enforce, or integrate with your app’s security workflow. |
| threat_scope | Streams threat intelligence to ThreatScope™ for monitoring and analytics without requiring in-app enforcement. |
| threat_memory | Persists additional Threat-Event™ history so the app can retain and reuse prior threat state over time. |
| match_API | Enables DeviceMATCH™ API calls to compare IDAnchor device/install/instance identities. |
| risk_API | Enables MobileRISK™ / session-risk API calls to score device and session risk from Appdome telemetry. |
Security Plumbing (Non-Defense)
| DefenseOS™ Plugin | Description |
| secure_keystore_bridge | Uses platform secure key storage (Android Keystore / iOS Keychain + Secure Enclave where applicable) for encryption/signing and enforces key protection properties. |
| crypto_work_dispatch | Dispatches crypto workloads safely/off-main-thread; supports batching and preferential hardware-backed primitives when available. |
| secure_persistent_state | AES-encrypts persistent runtime state stored in the app sandbox (e.g., posture state, tokens, flags). |
| hardened_shell_exec | Hardens command execution pathways (minimize usage, sanitize args, detect hijacked binaries/paths). |
| android_components_monitoring | Monitors Android component surface (Activities/Services/Receivers/Providers) for abnormal invocation patterns and tampering/bypass attempts. |
| ios_components_monitoring | Monitors iOS runtime/components (schemes, extensions boundaries, dynamic library behavior, lifecycle hooks) for abnormal patterns and tampering/bypass attempts. |
| robust_jni | Hardened JNI boundary (argument validation, safe loading, error isolation) to reduce crash/abuse surface and improve native interoperability. |
| openssl | Bundled OpenSSL crypto stack used by Appdome protections for secure cryptographic operations at runtime. |
| secure_packages_awareness | Maintains secure awareness of installed packages so detections can evaluate device app context without exposing raw package data insecurely. |
Related Articles:
- Using Certified Secure™ Android & iOS Apps Build Certification in DevOps CI/CD
- How to Understand Appdome Version Numbering
- How to Use DevSecOps Build System to Secure Mobile Apps at Scale
- How to Create and Manage Appdome Mobile App Protection Templates for Android & iOS Apps
How Do I Learn More?
If you have any questions, please send them our way at support.appdome.com or via the chat window on the Appdome platform, or feel free to request a demo at any time.
Thank you!
Thanks for visiting Appdome! Our mission is to secure every app on the planet by making mobile app security easy. We hope we’re living up to the mission with your project. If you don’t already have an account, you can sign up for free.