How to Protect Mobile Apps With Send IDAnchor on Demand Using AI
This Knowledge Base article describes how to use Appdome’s AI in your CI/CD pipeline to continuously deliver plugins that Protect IDAnchor on Demand in Mobile apps.
What is IDAnchor on Demand?
Send IDAnchor on Demand is an optional feature in Appdome’s IDAnchor™ suite that allows a mobile app to request the current device’s identity at any point during the app’s lifecycle. The identity—known as the IDAnchor value—is a unique, tamper-resistant fingerprint created from tampering-resistant details about the device and its environment.
Instead of waiting for a threat to trigger the retrieval of the IDAnchor, this feature gives you the ability to request it proactively—during login, account recovery, session validation, or any custom flow that requires verifying the device’s trust level. This flexibility is essential in fraud prevention, account takeover (ATO) defense, and transaction risk scoring, where real-time decisions rely on confirming whether the current device matches a previously trusted one.
How Appdome Protects Mobile Apps by Sending IDAnchor on Demand
Appdome’s dynamic Send IDAnchor on Demand plugin retrieves the device’s IDAnchor value whenever needed during runtime, and uses it for real-time trust checks, fraud analysis, and session control.
Below is a list of metadata that can be associated with each IDAnchor payload, true device attributes, and Advertising ID protections.
Fields consumable on demand
| Key | Description |
|---|---|
| DeviceID | The current IDAnchor value, as calculated for the device in the session. |
| DeviceIDState | Whether a reliable, consistent IDAnchor value could be established. Ready — a complete, accurate ID was generated; Initializing — a partial ID (signals still being processed). |
| previousDeviceID | The IDAnchor value calculated in the previous session on this device. |
| DeviceIDDetections | Security detections associated with the IDAnchor from the current session (semicolon-separated). When IDAnchor Session Risk is enabled. Learn More |
| installationID | The App Install ID — a unique ID for the app installation on the device. When App Install ID is enabled. Learn More |
| instanceID | The App Instance ID — a per app-instance identifier on the device. When App Instance ID is enabled. Learn More |
| releaseID | A unique identifier for each version of a mobile app. When App Release ID is enabled. Learn More |
| buildID | The Task ID of the Appdome build used to create this app version. When App Build ID is enabled. |
| teamFingerprint | The Team ID on the Appdome platform — an identifier for the DevOps workspace/team that initiated the app fuse. When DevOps Workspace Fingerprint is enabled. Learn More |
| gsfID (*Android only) | Google Services Framework (GSF) ID — a 16-character hexadecimal identifier assigned by Google when a user signs in with a Google account. When GSF ID is enabled. Learn More |
True Device Attributes Context Keys
Delivered when Trusted (True) Device Attributes is enabled.
| Key | Description |
|---|---|
| trueDeviceManufacturer | The device manufacturer, as determined and validated by Appdome. |
| trustDeviceManufacturer | Whether the device’s manufacturer attribute appears to be manipulated. Possible results: Safe or At-Risk. |
| trueDeviceModel | The model of the device, as determined and validated by Appdome. |
| trustDeviceModel | Whether the device’s model attribute appears to be manipulated. Possible results: Safe or At-Risk. |
| trueOsVersion | The OS version running on the device, as determined and validated by Appdome. |
| trustOsVersion | Whether the OS version appears to be manipulated. Possible results: Safe or At-Risk. |
| trueSdkVersion (*Android only) | The Android SDK version on the device, as determined and validated by Appdome. |
| trustSdkVersion (*Android only) | Whether the reported SDK version appears to be manipulated. Possible results: Safe or At-Risk. |
Authentication Attributes Context Keys
Delivered when Trusted (True) Device Attributes is enabled. for more info.
| Key | Description |
|---|---|
| trueBiometricStatus | Biometric enrollment state. Values: strongBiometricEnrolled, biometricEnrolled, noBiometricEnrolled, or N/A. |
| trustBiometricStatus | Whether the biometric status appears to be manipulated. Possible results: Safe or At-Risk. |
| trueLockingStatus | Device screen-lock state. Values: passcodeEnrolled, noPasscodeEnrolled, or N/A. |
| trustLockingStatus | Whether the locking status appears to be manipulated. Possible results: Safe or At-Risk. |
Advertising ID Protections Context Keys
Delivered when Protect Advertising IDs is enabled. for more info.
| Key | Description |
|---|---|
| trustGAID (*Android only) | Appdome’s assessment of whether the Google Advertising ID (GAID) has been tampered with. Possible results: Safe or At-Risk. |
| trustIDFA (*iOS only) | Appdome’s assessment of whether the Identifier for Advertisers (IDFA) has been tampered with. Possible results: Safe or At-Risk. |
| trustIDFV (*iOS only) | Appdome’s assessment of whether the Identifier for Vendors (IDFV) has been tampered with. Possible results: Safe or At-Risk. |
Device Geo Attributes Context Keys
Delivered when Device Geo Attributes is enabled. for more info.
| Key | Description |
|---|---|
| trueTimezone | The device timezone, as determined and validated by Appdome. |
| trueDeviceLanguage | The device language, as determined and validated by Appdome. |
| trueDeviceCountry | The device country (locale region), as determined and validated by Appdome. |
| trueCountry | The country derived from the device’s location, as determined and validated by Appdome. |
| trueLocality | The locality derived from the device’s location. |
| trueLatitude | The device latitude. |
| trueLongitude | The device longitude. |
| hasLocationPermission | Whether the app currently holds location permission. |
| lastLocationRetrieval | Timestamp of the last successful location retrieval. |
Use the code snippets below to retrieve the desired context keys’ values.
Android:
SharedPreferences sharedPreferences = PreferenceManager.getDefaultSharedPreferences(this);
String DeviceID = sharedPreferences.getString("DeviceID", null);
String DeviceIDDetections = sharedPreferences.getString("DeviceIDDetections", null);
String previousDeviceID = sharedPreferences.getString("previousDeviceID", null);
String installationID = sharedPreferences.getString("installationID", null);
String releaseID = sharedPreferences.getString("releaseID", null);
String teamFingerprint = sharedPreferences.getString("teamFingerprint", null);

String gsfID = sharedPreferences.getString("gsfID", null);

// True Device Attributes
String trueDeviceManufacturer = sharedPreferences.getString("trueDeviceManufacturer", null);
String trustDeviceManufacturer = sharedPreferences.getString("trustDeviceManufacturer", null);
String trueDeviceModel = sharedPreferences.getString("trueDeviceModel", null);
String trustDeviceModel = sharedPreferences.getString("trustDeviceModel", null);
String trueOsVersion = sharedPreferences.getString("trueOsVersion", null);
String trustOsVersion = sharedPreferences.getString("trustOsVersion", null);
String trueSdkVersion = sharedPreferences.getString("trueSdkVersion", null);
String trustSdkVersion = sharedPreferences.getString("trustSdkVersion", null);

// Protect Advertising IDs
String trustGAID = sharedPreferences.getString("trustGAID", null);
iOS:
NSString *DeviceID = [[NSUserDefaults standardUserDefaults] stringForKey:@"DeviceID"];
NSString *DeviceIDDetections = [[NSUserDefaults standardUserDefaults] stringForKey:@"DeviceIDDetections"];
NSString *previousDeviceID = [[NSUserDefaults standardUserDefaults] stringForKey:@"previousDeviceID"];
NSString *installationID = [[NSUserDefaults standardUserDefaults] stringForKey:@"installationID"];
NSString *releaseID = [[NSUserDefaults standardUserDefaults] stringForKey:@"releaseID"];
NSString *teamFingerprint = [[NSUserDefaults standardUserDefaults] stringForKey:@"teamFingerprint"];

// True Device Attributes
NSString *trueDeviceManufacturer = [[NSUserDefaults standardUserDefaults] stringForKey:@"trueDeviceManufacturer"];
NSString *trustDeviceManufacturer = [[NSUserDefaults standardUserDefaults] stringForKey:@"trustDeviceManufacturer"];
NSString *trueDeviceModel = [[NSUserDefaults standardUserDefaults] stringForKey:@"trueDeviceModel"];
NSString *trustDeviceModel = [[NSUserDefaults standardUserDefaults] stringForKey:@"trustDeviceModel"];
NSString *trueOsVersion = [[NSUserDefaults standardUserDefaults] stringForKey:@"trueOsVersion"];
NSString *trustOsVersion = [[NSUserDefaults standardUserDefaults] stringForKey:@"trustOsVersion"];
Prerequisites for Using Appdome's Send IDAnchor on Demand Plugins:
To use Appdome’s mobile app security build system to Protect IDAnchor on Demand , you’ll need:
- Appdome account (create a free Appdome account here)
- A license for Send IDAnchor on Demand
- Mobile App (.ipa for iOS, or .apk or .aab for Android)
- Signing Credentials (see Signing Secure Android apps and Signing Secure iOS apps)
How to Implement Protect IDAnchor on Demand in Mobile Apps Using Appdome
On Appdome, follow these 3 simple steps to create self-defending Mobile Apps that Protect IDAnchor on Demand without an SDK or gateway:
-
Designate the Mobile App to be protected.
-
Upload an app via the Appdome Mobile Defense platform GUI or via Appdome’s DEV-API or CI/CD Plugins.
-
Mobile App Formats: .ipa for iOS, or .apk or .aab for Android
-
Send IDAnchor on Demand is compatible with: Obj-C, Java, JS, C#, C++, Swift, Kotlin, Flutter, React Native, Unity, Xamarin, and more.
-
-
Select the defense: Send IDAnchor on Demand.
-
-
Follow the steps in Sections 2.2-2.2.2 of this article to add the Send IDAnchor on Demand feature to your Fusion Set via the Appdome Console.
-
When you select the Send IDAnchor on Demand you'll notice that the Fusion Set you created in step 2.1 now bears the icon of the protection category that contains Send IDAnchor on Demand.
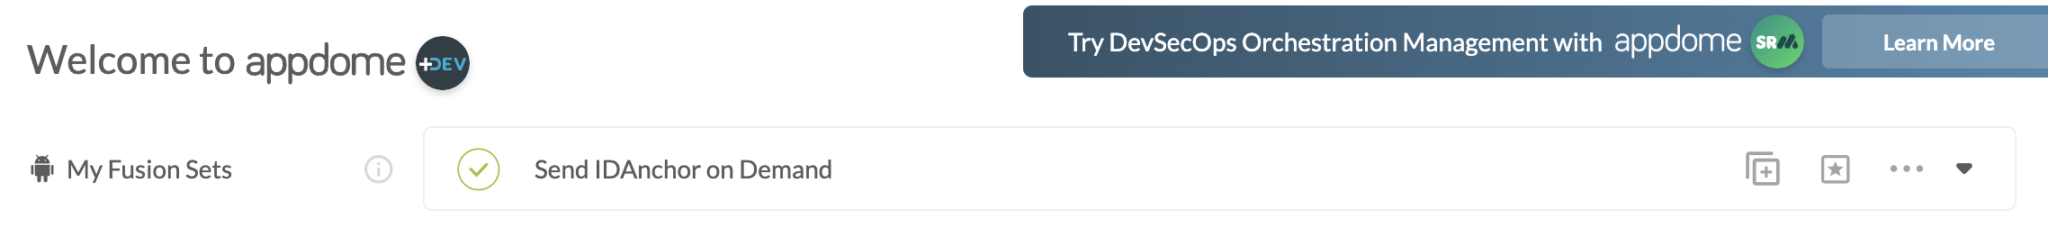
Figure 2: Fusion Set that displays the newly added Send IDAnchor on Demand protection
Note: Annotating the Fusion Set to identify the protection(s) selected is optional only (not mandatory). -
Open the Fusion Set Detail Summary by clicking the “...” symbol on the far-right corner of the Fusion Set. Copy the Fusion Set ID from the Fusion Set Detail Summary (as shown below):
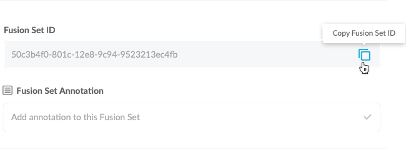
Figure 3: Fusion Set Detail Summary
-
Follow the instructions below to use the Fusion Set ID inside any standard mobile DevOps or CI/CD toolkit like Bitrise, Jenkins, Travis, Team City, Circle CI or other system:
-
Refer to the Appdome API Reference Guide for API building instructions.
-
Look for sample APIs in Appdome’s GitHub Repository.
-
Create and name the Fusion Set (security template) that will contain the Send IDAnchor on Demand feature as shown below: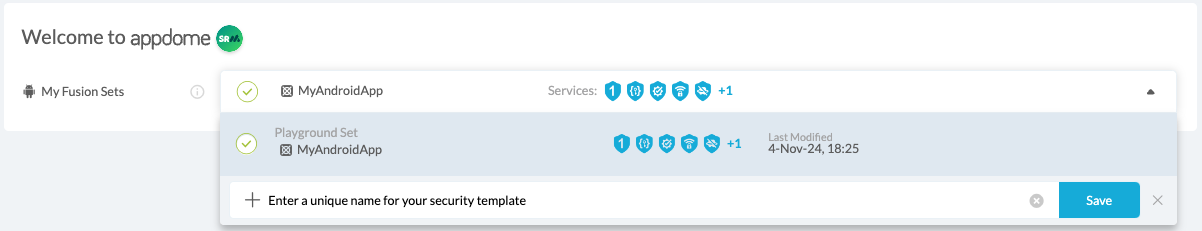
Figure 1: Fusion Set that will contain the Send IDAnchor on Demand feature
-
-
Add the Send IDAnchor on Demand feature to your security template.
-
Navigate to Build > IDAnchor tab > Android IDAnchor section in the Appdome Console.
-
Toggle On > Send IDAnchor on Demand.
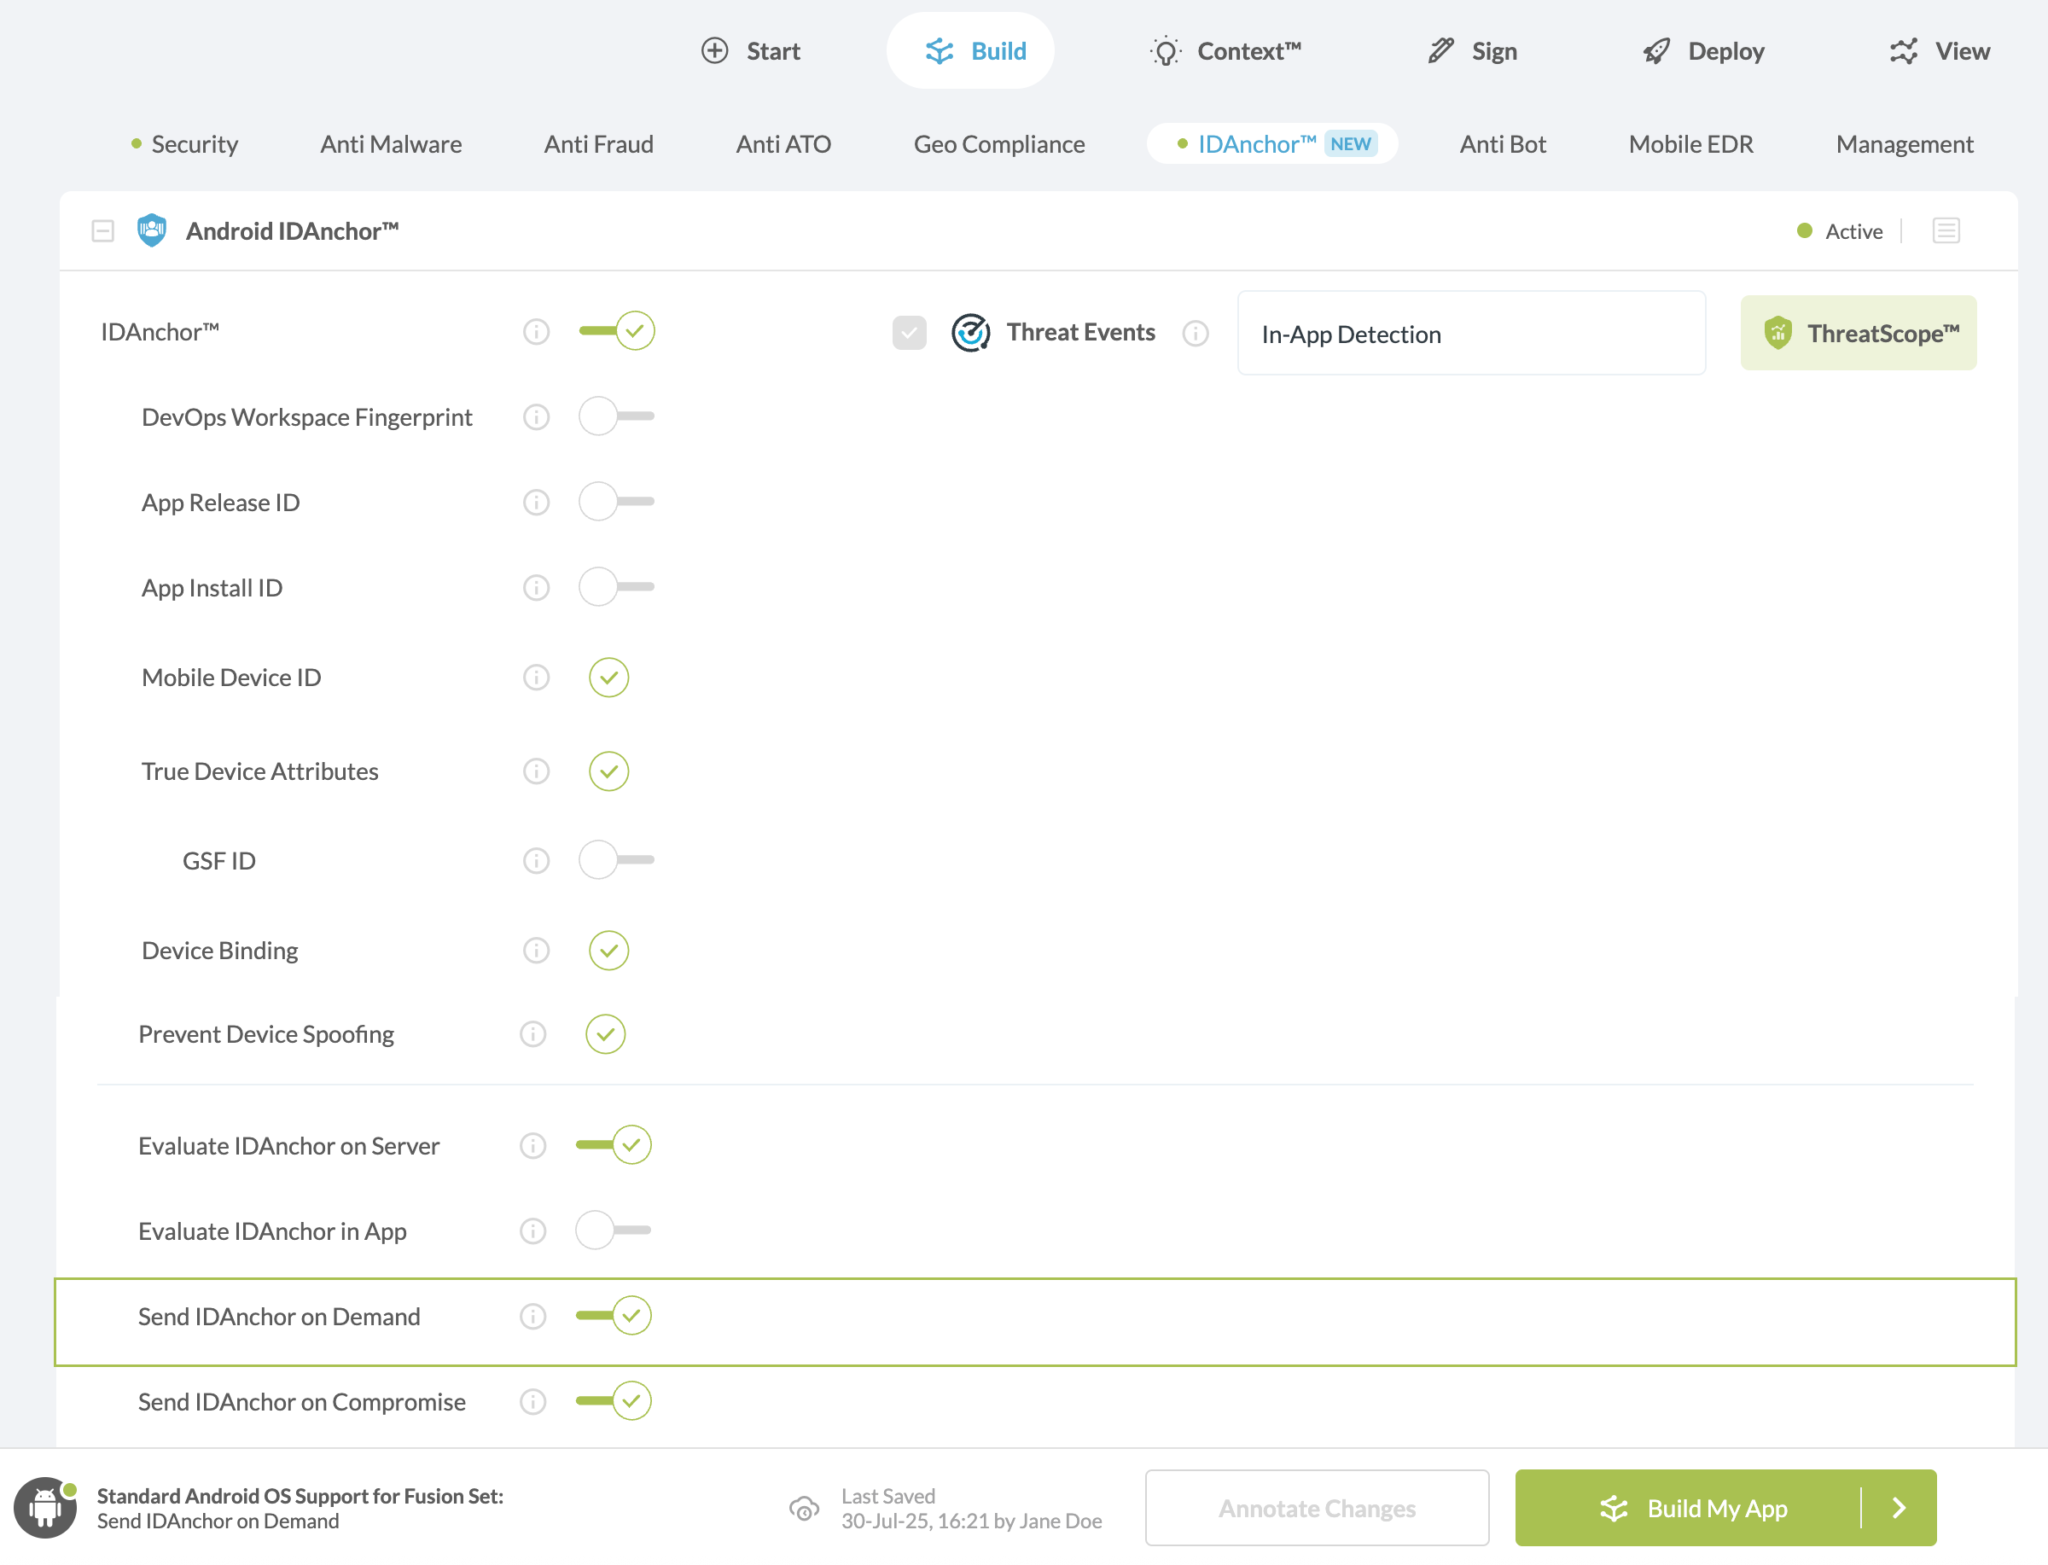
Figure 4: Selecting Protect IDAnchor on Demand
-
Congratulations! The Send IDAnchor on Demand protection is now added to the mobile app -
-
Certify the Send IDAnchor on Demand feature in Mobile Apps
After building Send IDAnchor on Demand, Appdome generates a Certified Secure™ certificate to guarantee that the Send IDAnchor on Demand protection has been added and is protecting the app. To verify that the Send IDAnchor on Demand protection has been added to the mobile app, locate the protection in the Certified Secure™ certificate as shown below:
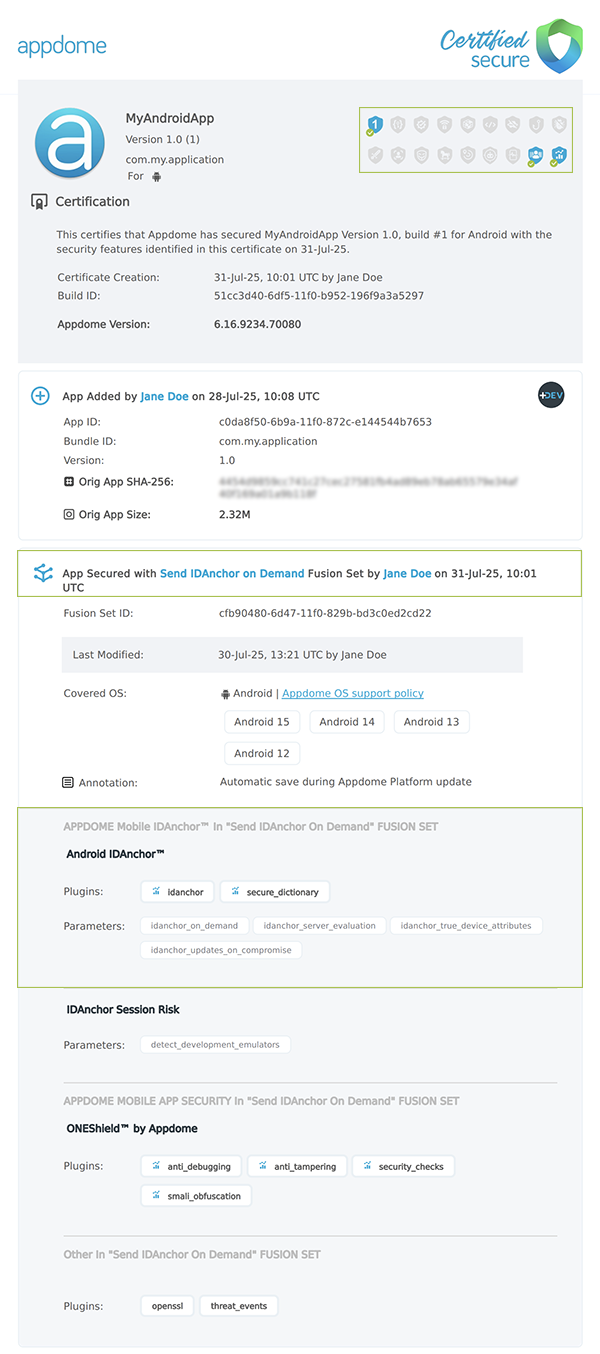
Figure 5: Certified Secure™ certificate
Each Certified Secure™ certificate provides DevOps and DevSecOps organizations the entire workflow summary, audit trail of each build, and proof of protection that Send IDAnchor on Demand has been added to each Mobile app. Certified Secure provides instant and in-line DevSecOps compliance certification that Send IDAnchor on Demand and other mobile app security features are in each build of the mobile app.
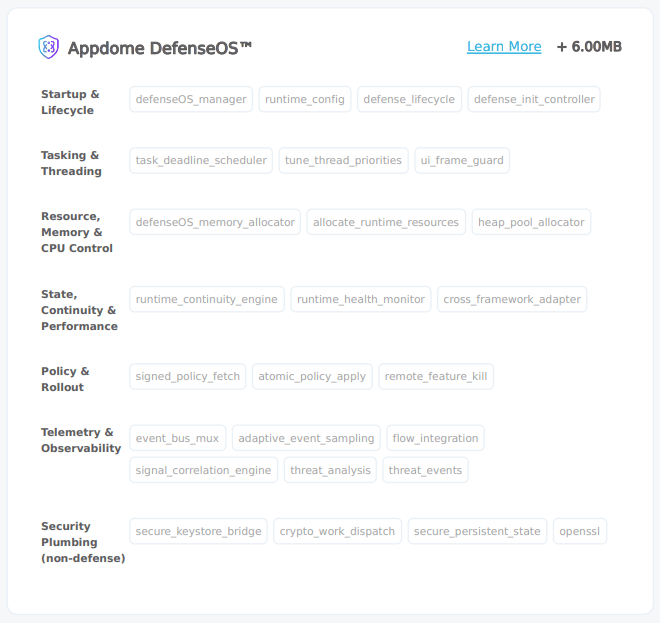
Figure 6: DefenseOS™
DefenseOS™ manages and coordinates Appdome defense capabilities in protected mobile apps. To learn more about DefenseOS and its runtime modules, see Understanding DefenseOS™.
Using Threat-Events™ for IDAnchor on Demand Intelligence and Control in Mobile Apps
Appdome Threat-Events™ provides consumable in-app mobile app attack intelligence and defense control when IDAnchor on Demand is detected. To consume and use Threat-Events™ for IDAnchor on Demand in Mobile Apps, use AddObserverForName in Notification Center, and the code samples for Threat-Events™ for IDAnchor on Demand shown below.
The specifications and options for Threat-Events™ for IDAnchor on Demand are:
| Threat-Event™ Elements | Protect IDAnchor on Demand Method Detail |
|---|---|
| Appdome Feature Name | Send IDAnchor on Demand |
| Threat-Event Mode | |
| OFF, IN-APP DEFENSE | Appdome detects, defends and notifies user (standard OS dialog) using customizable messaging. |
| ON, IN-APP DETECTION | Appdome detects the attack or threat and passes the event in a standard format to the app for processing (app chooses how and when to enforce). |
| ON, IN-APP DEFENSE | Uses Appdome Enforce mode for any attack or threat and passes the event in a standard format to the app for processing (gather intel on attacks and threats without losing any protection). |
| Certified Secure™ Threat Event Check | x |
| Visible in ThreatScope™ | x |
| Developer Parameters for Protecting IDAnchor on Demand Threat-Event™ | |
| Threat-Event NAME | |
| Threat-Event DATA | reasonData |
| Threat-Event CODE | reasonCode |
| Threat-Event SCORE | |
| currentThreatEventScore | Current Threat-Event score |
| threatEventsScore | Total Threat-events score |
| Threat-Event Context Keys | |
|---|---|
| Timestamp | The exact time the threat event was triggered, recorded in milliseconds since epoch |
| message | Message displayed for the user on event |
| externalID | The external ID of the event which can be listened via Threat Events |
| osVersion | OS version of the current device |
| deviceModel | Current device model |
| deviceManufacturer | The manufacturer of the current device |
| fusedAppToken | The task ID of the Appdome fusion of the currently running app |
| kernelInfo | Info about the kernel: system name, node name, release, version and machine. |
| carrierPlmn | PLMN of the device. Only available for Android devices. |
| deviceID | Current device ID |
| reasonCode | Reason code of the occurred event |
| deviceBrand | Brand of the device |
| deviceBoard | Board of the device |
| buildUser | Build user |
| buildHost | Build host |
| sdkVersion | Sdk version |
| threatCode | The last six characters of the threat code specify the OS, allowing the Threat Resolution Center to address the attack on the affected device. |
With Threat-Events™ enabled (turned ON), Mobile developers can get detailed attack intelligence and granular defense control in Mobile applications and create amazing user experiences for all mobile end users when IDAnchor on Demand is detected.
The following is a code sample for native Mobile apps, which uses all values in the specification above for Send IDAnchor on Demand:
Important! Replace all placeholder instances of <Context Key> with the specific name of your threat event context key across all language examples. This is crucial to ensure your code functions correctly with the intended event data. For example, The <Context Key> could be the message, externalID, OS Version, reason code, etc.
xxxxxxxxxxIntentFilter intentFilter = new IntentFilter();intentFilter.addAction("");BroadcastReceiver threatEventReceiver = new BroadcastReceiver() { public void onReceive(Context context, Intent intent) { String message = intent.getStringExtra("message"); // Message shown to the user String reasonData = intent.getStringExtra("reasonData"); // Threat detection cause String reasonCode = intent.getStringExtra("reasonCode"); // Event reason code // Current threat event score String currentThreatEventScore = intent.getStringExtra("currentThreatEventScore"); // Total threat events score String threatEventsScore = intent.getStringExtra("threatEventsScore"); // Replace '<Context Key>' with your specific event context key // String variable = intent.getStringExtra("<Context Key>"); // Your logic goes here (Send data to Splunk/Dynatrace/Show Popup...) }};if (Build.VERSION.SDK_INT >= Build.VERSION_CODES.TIRAMISU) { registerReceiver(threatEventReceiver, intentFilter, Context.RECEIVER_NOT_EXPORTED);} else { registerReceiver(threatEventReceiver, intentFilter);}xxxxxxxxxxval intentFilter = IntentFilter()intentFilter.addAction("")val threatEventReceiver = object : BroadcastReceiver() { override fun onReceive(context: Context?, intent: Intent?) { var message = intent?.getStringExtra("message") // Message shown to the user var reasonData = intent?.getStringExtra("reasonData") // Threat detection cause var reasonCode = intent?.getStringExtra("reasonCode") // Event reason code // Current threat event score var currentThreatEventScore = intent?.getStringExtra("currentThreatEventScore") // Total threat events score var threatEventsScore = intent?.getStringExtra("threatEventsScore") // Replace '<Context Key>' with your specific event context key // var variable = intent?.getStringExtra("<Context Key>") // Your logic goes here (Send data to Splunk/Dynatrace/Show Popup...) }}if (Build.VERSION.SDK_INT >= Build.VERSION_CODES.TIRAMISU) { registerReceiver(threatEventReceiver, intentFilter, Context.RECEIVER_NOT_EXPORTED)} else { registerReceiver(threatEventReceiver, intentFilter)}x
let center = NotificationCenter.defaultcenter.addObserver(forName: Notification.Name(""), object: nil, queue: nil) { (note) in guard let usrInf = note.userInfo else { return } let message = usrInf["message"]; // Message shown to the user let reasonData = usrInf["reasonData"]; // Threat detection cause let reasonCode = usrInf["reasonCode"]; // Event reason code // Current threat event score let currentThreatEventScore = usrInf["currentThreatEventScore"]; // Total threat events score let threatEventsScore = usrInf["threatEventsScore"]; // Replace '<Context Key>' with your specific event context key // let variable = usrInf["<Context Key>"]; // Your logic goes here (Send data to Splunk/Dynatrace/Show Popup...)}xxxxxxxxxx[[NSNotificationCenter defaultCenter] addObserverForName: @"" object:nil queue:nil usingBlock:^(NSNotification *org_note) { __block NSNotification *note = org_note; dispatch_async(dispatch_get_main_queue(), ^(void) { // Message shown to the user NSString *message = [[note userInfo] objectForKey:@"message"]; // Threat detection cause NSString *reasonData = [[note userInfo] objectForKey:@"reasonData"]; // Event reason code NSString *reasonCode = [[note userInfo] objectForKey:@"reasonCode"]; // Current threat event score NSString *currentThreatEventScore = [[note userInfo] objectForKey:@"currentThreatEventScore"]; // Total threat events score NSString *threatEventsScore = [[note userInfo] objectForKey:@"threatEventsScore"]; // Replace '<Context Key>' with your specific event context key // NSString *variable = [[note userInfo] objectForKey:@"<Context Key>"]; // Your logic goes here (Send data to Splunk/Dynatrace/Show Popup...) });}];xxxxxxxxxxconst { ADDevEvents } = NativeModules;const aDDevEvents = new NativeEventEmitter(ADDevEvents);function registerToDevEvent(action, callback) { NativeModules.ADDevEvents.registerForDevEvent(action); aDDevEvents.addListener(action, callback);}export function registerToAllEvents() { registerToDevEvent( "", (userinfo) => Alert.alert(JSON.stringify(userinfo)) var message = userinfo["message"] // Message shown to the user var reasonData = userinfo["reasonData"] // Threat detection cause var reasonCode = userinfo["reasonCode"] // Event reason code // Current threat event score var currentThreatEventScore = userinfo["currentThreatEventScore"] // Total threat events score var threatEventsScore = userinfo["threatEventsScore"] // Replace '<Context Key>' with your specific event context key // var variable = userinfo["<Context Key>"] // Your logic goes here (Send data to Splunk/Dynatrace/Show Popup...) );}x
RegisterReceiver(new ThreatEventReceiver(), new IntentFilter("")); class ThreatEventReceiver : BroadcastReceiver{ public override void OnReceive(Context context, Intent intent) { // Message shown to the user String message = intent.GetStringExtra("message"); // Threat detection cause String reasonData = intent.GetStringExtra("reasonData"); // Event reason code String reasonCode = intent.GetStringExtra("reasonCode"); // Current threat event score String currentThreatEventScore = intent.GetStringExtra("currentThreatEventScore"); // Total threat events score String threatEventsScore = intent.GetStringExtra("threatEventsScore"); // Replace '<Context Key>' with your specific event context key // String variable = intent.GetStringExtra("<Context Key>"); // Your logic goes here (Send data to Splunk/Dynatrace/Show Popup...) }}x
NSNotificationCenter.DefaultCenter.AddObserver( (NSString)"", // Threat-Event Identifier delegate (NSNotification notification) { // Message shown to the user var message = notification.UserInfo.ObjectForKey("message"); // Threat detection cause var reasonData = notification.UserInfo.ObjectForKey("reasonData"); // Event reason code var reasonCode = notification.UserInfo.ObjectForKey("reasonCode"); // Current threat event score var currentThreatEventScore = notification.UserInfo.ObjectForKey("currentThreatEventScore"); // Total threat events score var threatEventsScore = notification.UserInfo.ObjectForKey("threatEventsScore"); // Replace '<Context Key>' with your specific event context key // var variable = notification.UserInfo.ObjectForKey("<Context Keys>"); // Your logic goes here (Send data to Splunk/Dynatrace/Show Popup...) });xxxxxxxxxxwindow.broadcaster.addEventListener("", function(userInfo) { var message = userInfo.message // Message shown to the user var reasonData = userInfo.reasonData // Threat detection cause var reasonCode = userInfo.reasonCode // Event reason code // Current threat event score var currentThreatEventScore = userInfo.currentThreatEventScore // Total threat events score var threatEventsScore = userInfo.threatEventsScore // Replace '<Context Key>' with your specific event context key // var variable = userInfo.<Context Keys> // Your logic goes here (Send data to Splunk/Dynatrace/Show Popup...)});x
import 'dart:async';import 'package:flutter/material.dart';import 'package:flutter/services.dart';class PlatformChannel extends StatefulWidget { const PlatformChannel({super.key}); State<PlatformChannel> createState() => _PlatformChannelState();}class _PlatformChannelState extends State<PlatformChannel> { // Replace with your EventChannel name static const String _eventChannelName = ""; static const EventChannel _eventChannel = EventChannel(_eventChannelName); void initState() { super.initState(); _eventChannel.receiveBroadcastStream().listen(_onEvent, onError: _onError); } void _onEvent(Object? event) { setState(() { // Adapt this section based on your specific event data structure var eventData = event as Map; // Example: Accessing 'externalID' field from the event var externalID = eventData['externalID']; // Customize the rest of the fields based on your event structure String message = eventData['message']; // Message shown to the user String reasonData = eventData['reasonData']; // Threat detection cause String reasonCode = eventData['reasonCode']; // Event reason code // Current threat event score String currentThreatEventScore = eventData['currentThreatEventScore']; // Total threat events score String threatEventsScore = eventData['threatEventsScore']; // Replace '<Context Key>' with your specific event context key // String variable = eventData['<Context Keys>']; }); } // Your logic goes here (Send data to Splunk/Dynatrace/Show Popup...)}Using Appdome, there are no development or coding prerequisites to build secured Mobile Apps by using Send IDAnchor on Demand. There is no SDK and no library to code or implement in the app and no gateway to deploy in your network. All protections are built into each app and the resulting app is self-defending and self-protecting.
Releasing and Publishing Mobile Apps with Send IDAnchor on Demand
After successfully securing your app by using Appdome, there are several available options to complete your project, depending on your app lifecycle or workflow. These include:
- Customizing, Configuring & Branding Secure Mobile Apps.
- Deploying/Publishing Secure mobile apps to Public or Private app stores.
- Releasing Secured Android & iOS Apps built on Appdome.
Related Articles:
- How to Protect iOS Apps With IDAnchor Using AI
- How to Protect Android Apps With IDAnchor Using AI
- How to Protect Mobile Apps With Mobile Device ID Using AI
How Do I Learn More?
If you have any questions, please send them our way at support.appdome.com or via the chat window on the Appdome platform.
Thank you!
Thanks for visiting Appdome! Our mission is to secure every app on the planet by making mobile app security easy. We hope we’re living up to the mission with your project.